Most security pages in this industry look the same. A row of certification logos near the top. A paragraph about "bank-level encryption." A list of adjectives: secure, trusted, enterprise-grade. None of it is technically false, and none of it tells you anything you can actually check. We built something different, and it took longer to write than a normal trust page would have.
Most security pages sell confidence, not information
A badge tells you a vendor passed an audit at some point. It doesn't tell you what was audited, when, or whether the specific claim you care about was even in scope. That's not always dishonest. It's just a format that optimizes for looking trustworthy rather than being checkable. We wanted something a practice's own compliance officer could actually verify against, not just read and take on faith.
What a ledger does that a badge can't
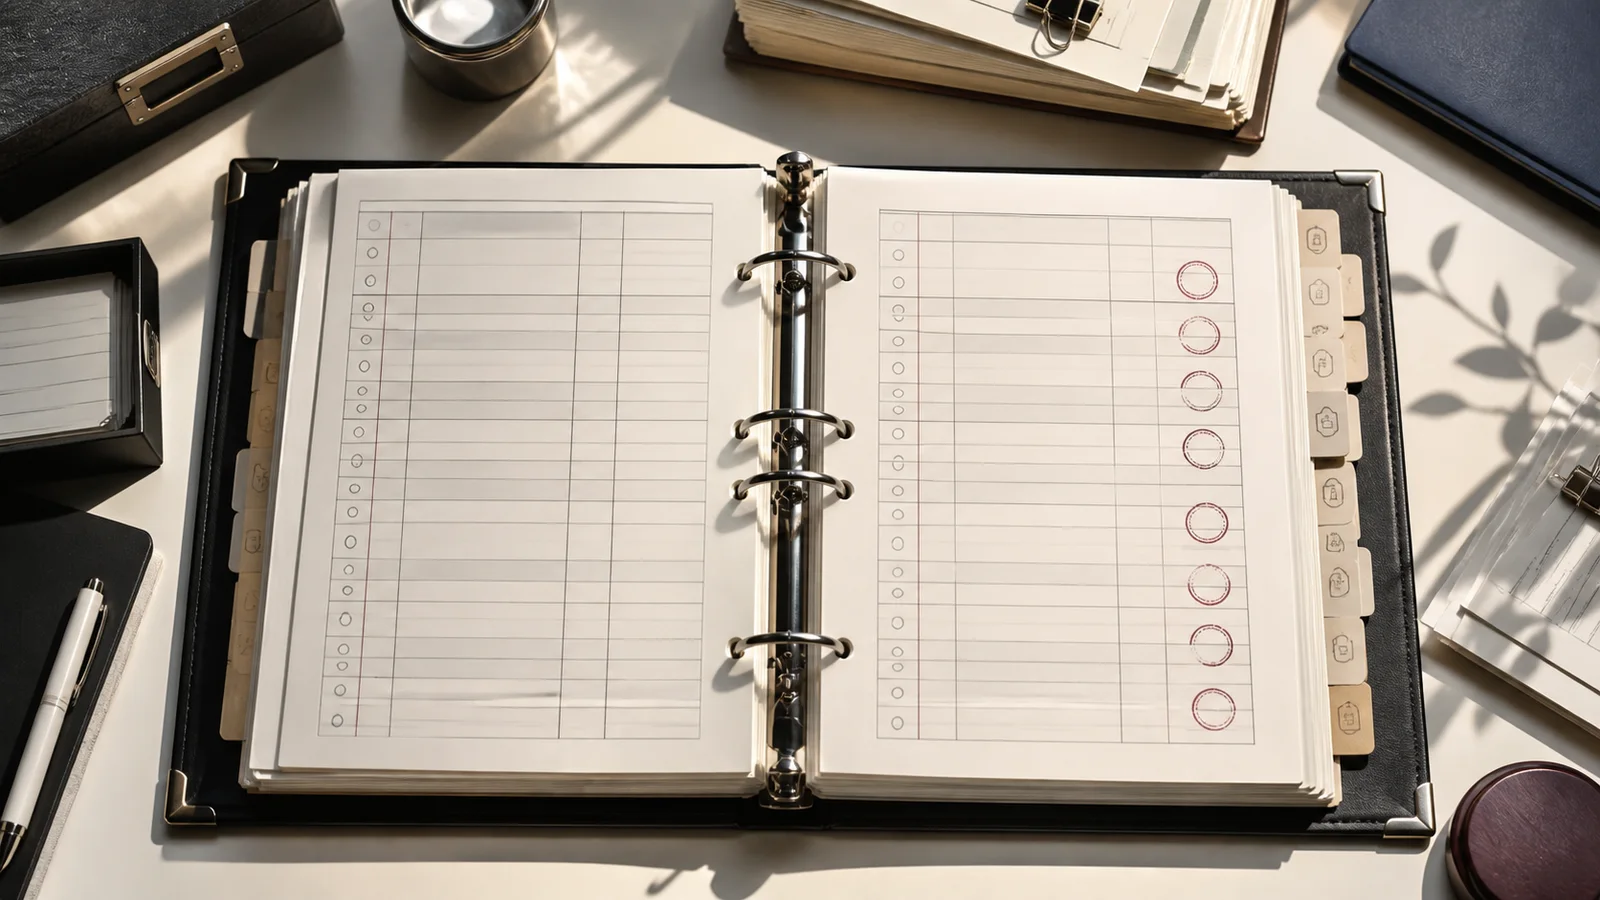
Our security ledger lists individual claims, not a general impression. Each row has a scope (which plans it applies to), a source (where the claim comes from), a last-verified date, and a status: confirmed, pending validation, or limited. If you click a row, it expands into the actual detail instead of stopping at the headline.
That structure forces a kind of honesty a badge doesn't. You can't write a vague, reassuring sentence and call it a row. You either have a specific, sourced claim, or you mark the row pending and say so.
What it costs to do it this way
It means our security page has gaps other companies would paper over. We're not SOC 2 Type II or HITRUST certified yet, and instead of writing something that implies otherwise, we have a row that says exactly that. It means our pricing page shows a real number instead of "contact sales" theater, because we'd rather be checked against it than protected by vagueness.
It also means slower writing. A badge takes an afternoon to design. A ledger takes ongoing work to keep accurate, because every claim has to trace back to something real before it goes up, and someone has to notice when it goes stale.
The parts we still mark pending
We don't have a public subprocessor list yet. That's an open item on the ledger, not a secret. If it's decision-relevant for your practice, ask us directlyand we'll give you a real answer instead of a placeholder.